Workday AED integration status
People and site data. ReadyAED publishes no confirmed Workday connection today.
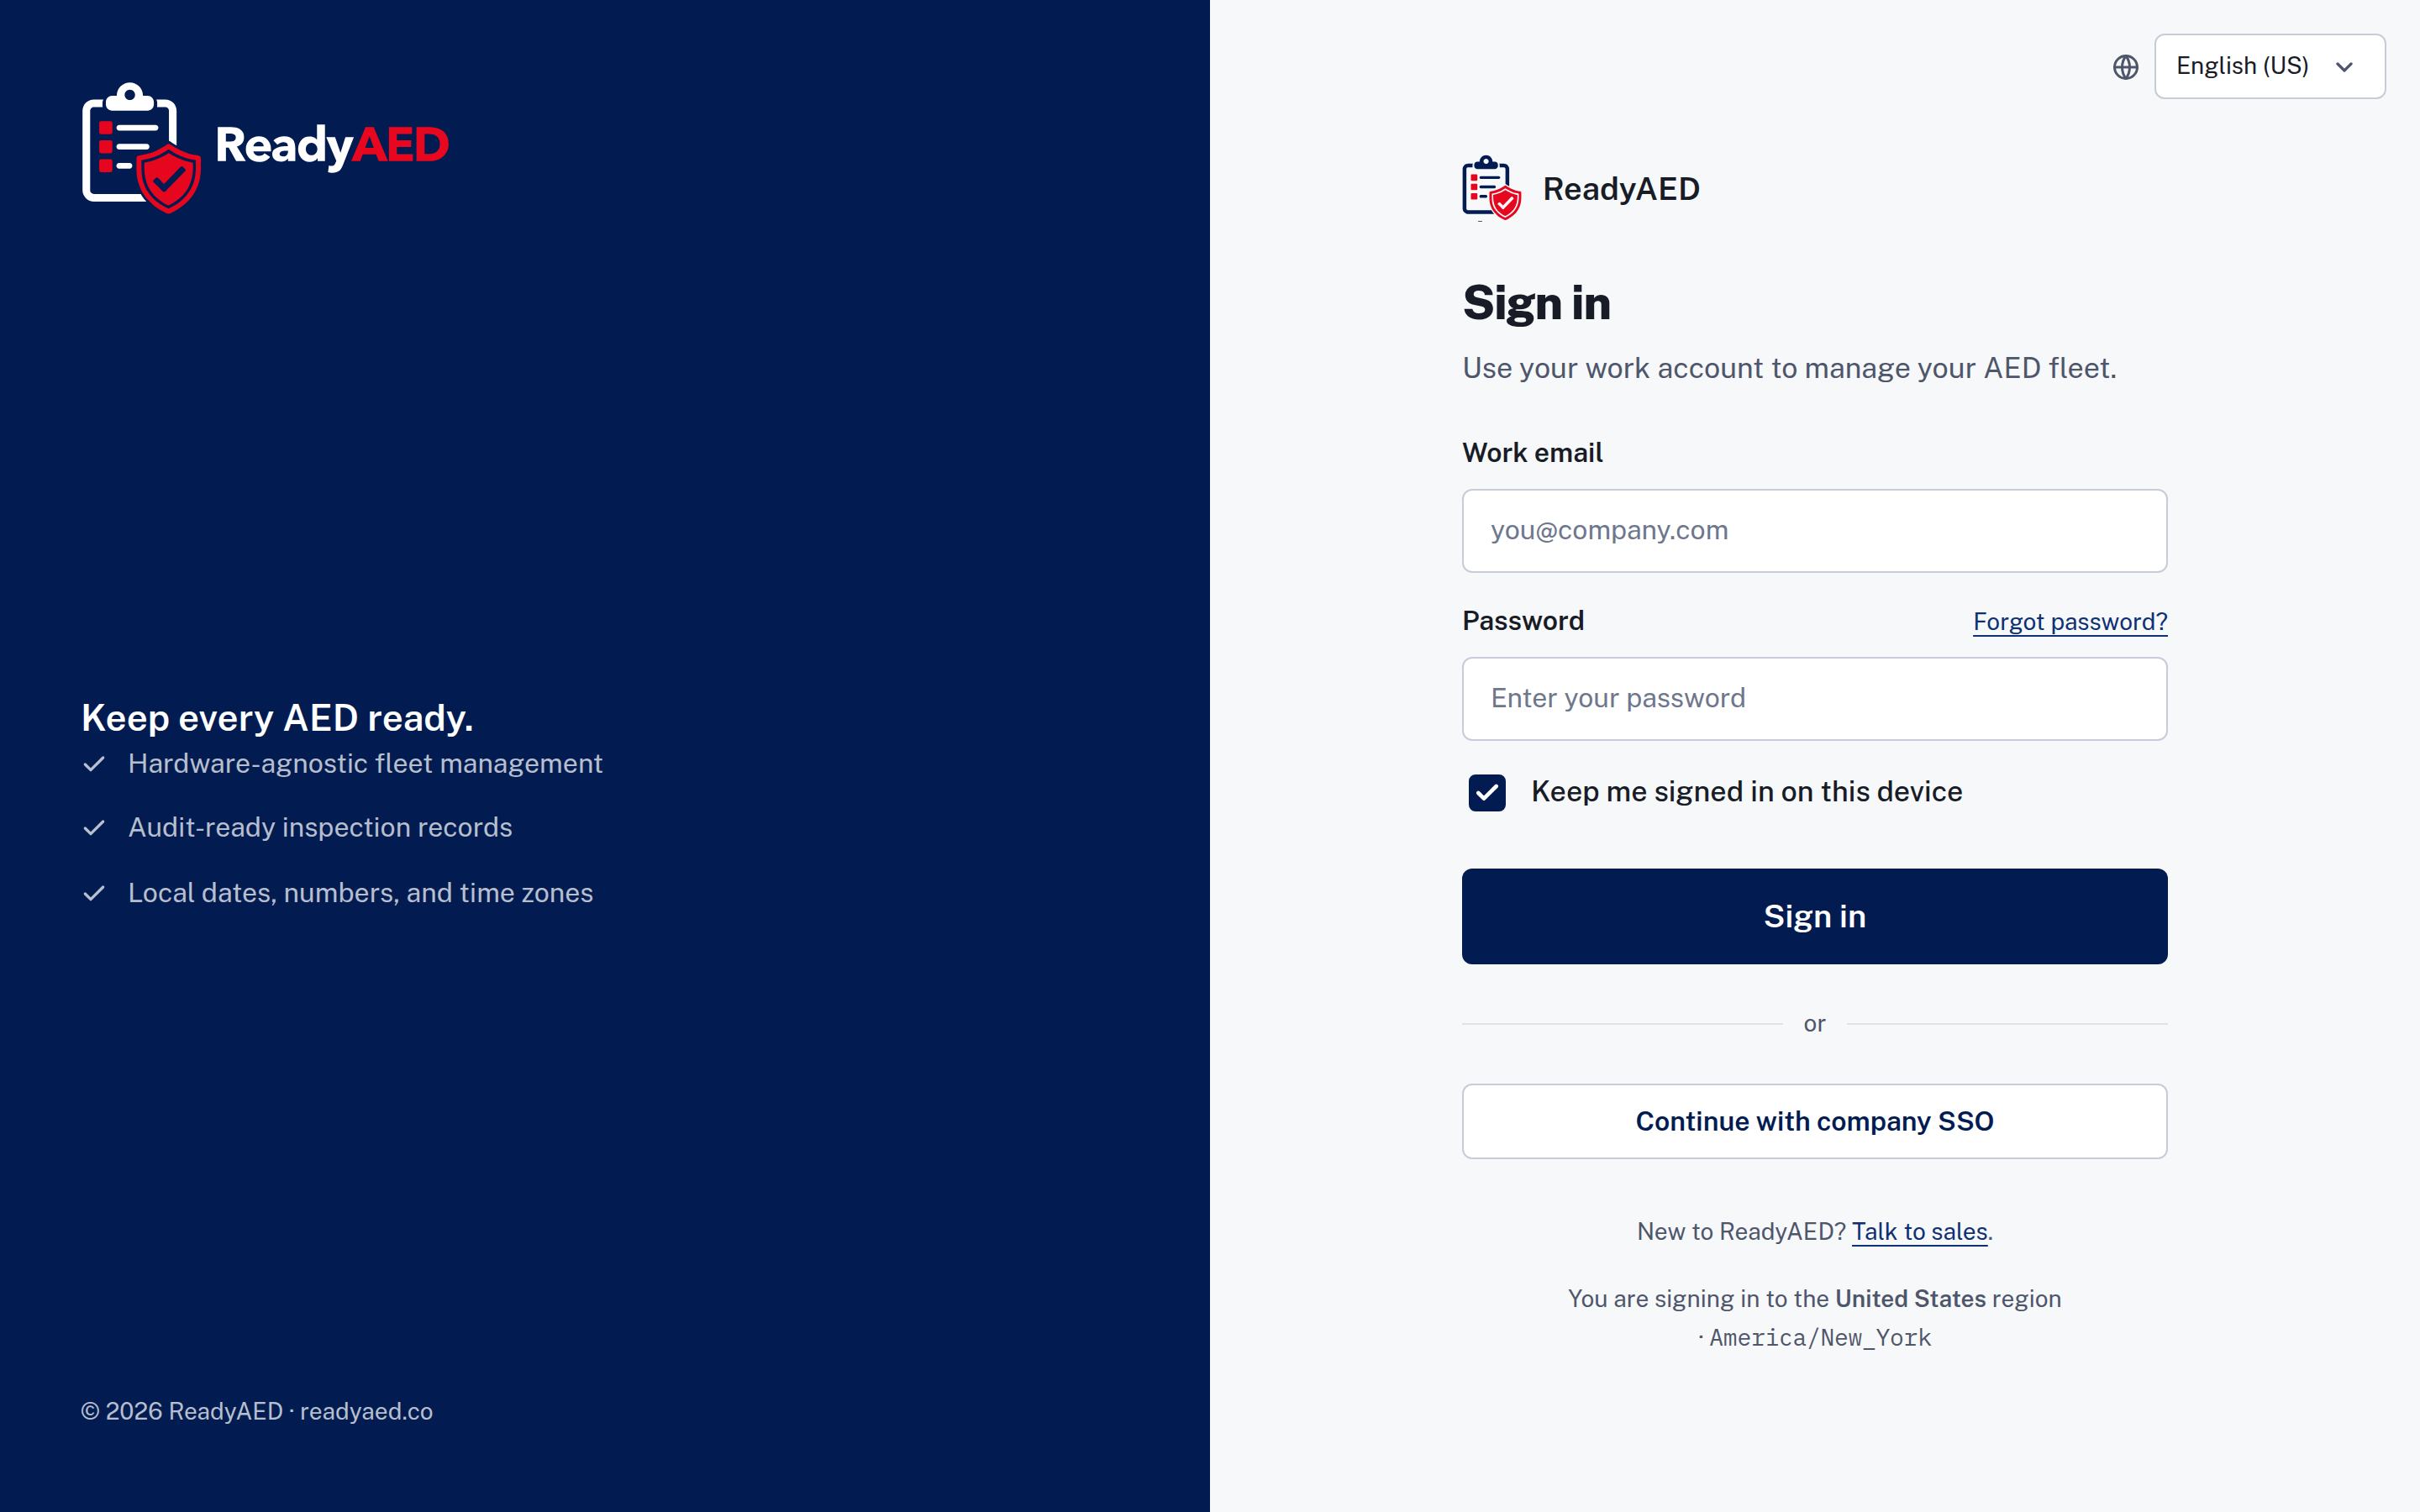
Company SSO (single sign-on) is on the sign-in screen today. ReadyAED does not name identity providers, and it publishes no Okta connection.
Okta is an identity provider. An identity provider is a service that manages sign-in and access for a company.
ReadyAED is not affiliated with, endorsed by or sponsored by Okta. All marks belong to their owners. this passage needs legal sign-off
ReadyAED is an AED (automated external defibrillator) readiness and compliance platform. This page is for the IT and security team that reviews the AED program with the rest of the estate.
ReadyAED publishes no confirmed Okta connection today. product confirmation of REST API, webhooks and HRIS/EHS integrations, with named systems
One sign-in for the program, managed with the rest of the company.
A security review covers the AED program even when the program is small. The reviewer asks how staff sign in, who can see the records and what happens when a person leaves. A separate password for the AED software answers none of those questions well.
The AED program is one system in that review. The program still needs the same answers as the systems around it.
A separate password adds one more account to manage. The site team remembers one more password, and the reviewer adds one more exception to the list.
A leaver keeps access until someone removes the account. Nobody sees the removal in a spreadsheet of AEDs.
Company SSO adds a second sign-in path. Work email and password still work, and ReadyAED shows company SSO on the sign-in screen today.
The identity providers behind company SSO are not published. named SSO identity providers, if any
If your team runs Okta, the open question is whether Okta can be the provider. ReadyAED publishes that answer only after the product team confirms it. product confirmation of REST API, webhooks and HRIS/EHS integrations, with named systems
The same review asks about records. The audit trail records user and system events, device history and inspection history. Your team exports the report, a CSV (comma-separated values) file and a device history.
An access review asks for a list of people with access and the date of the last review. ReadyAED publishes no access list and no review date. confirmed role and permission model The account shows invited site staff, a site custodian and a last inspector. Devices are assigned to a person. A directory connection is one way to keep that list in step with the company directory. ReadyAED publishes no such connection. product confirmation of REST API, webhooks and HRIS/EHS integrations, with named systems
Company SSO today. Nothing else is published.
| Area | What ReadyAED provides today | Status |
|---|---|---|
| Sign-in | Work email and password, or Continue with company SSO | Confirmed |
| Identity providers | Not named | named SSO identity providers, if any |
| Directory connection | Not published | product confirmation of REST API, webhooks and HRIS/EHS integrations, with named systems |
| MFA and encryption | Not confirmed | confirmation of security controls (MFA, encryption) |
| Role and permission model | Not published | confirmed role and permission model |
Your team signs in with a work email and a password. A forgot-password path and a keep-me-signed-in option are available.
Company SSO is also available. New organizations go to sales, so the product has no self-serve signup screen.
Site staff are invited into the account. The record shows a site custodian (the person who looks after a site) and the last inspector. Devices are assigned to a person. confirmed role and permission model
The audit trail records user and system events, device history and inspection history.
No interface details are published for Okta.
ReadyAED publishes no API keys, endpoints, webhooks or connection list. product confirmation of REST API, webhooks and HRIS/EHS integrations, with named systems confirmed integration list — product confirmation required
The API and integration status page states the interfaces that are confirmed today. The Security & Trust Center states the security and compliance posture.
Company SSO is the only demonstrated part of the open-by-design position.
The Integrations hub groups every published page by category. The other pages cover three more systems.
People and site data. ReadyAED publishes no confirmed Workday connection today.
Service requests and incidents. ReadyAED publishes no confirmed ServiceNow connection today.
Team messages. ReadyAED publishes no confirmed Slack connection today.
See the sign-in screen, the register and the audit trail. Bring the identity question your security review asks. The product team confirms each interface before ReadyAED publishes it. product confirmation of REST API, webhooks and HRIS/EHS integrations, with named systems